OAuth articles
16 articles · Connected apps, the OAuth flows, and token handling.
 Integration
Salesforce Refresh Token Expiration: 30-Day Idle Fix
Salesforce now expires any OAuth refresh token left unused for 30 days, and enforcement began rolling out to production...
 Integration
Salesforce Instanced URL Enforcement: Remove Hardcoded Hosts
Salesforce instanced URL enforcement already blocks sandbox API calls sent to the wrong instance host, and production...
 Integration
OAuth User-Agent Flow Retirement: Move to Web Server + PKCE
On February 20, 2027 Salesforce stops issuing tokens through the user-agent and hybrid user-agent flows, which SPAs,...
 Integration
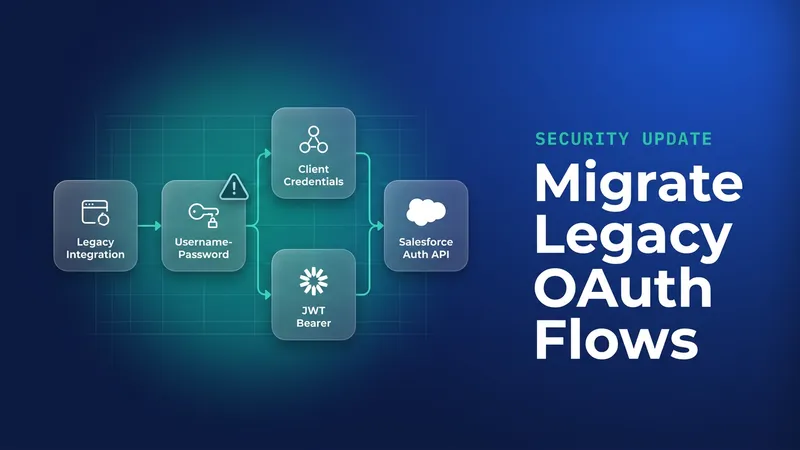
OAuth Username-Password Flow Retirement: Migrate by Feb 20
Salesforce blocks new tokens from the OAuth username-password flow on February 20, 2027, and affected integrations fail...
 Integration
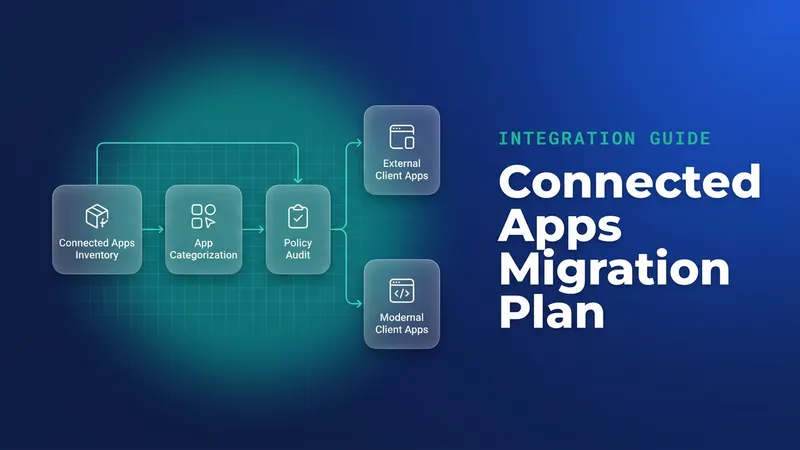
Connected Apps End of Support: What to Migrate and When
Connected apps end of support lands in Summer '27 for every app in your org, and device-flow apps face an earlier...
 Integration
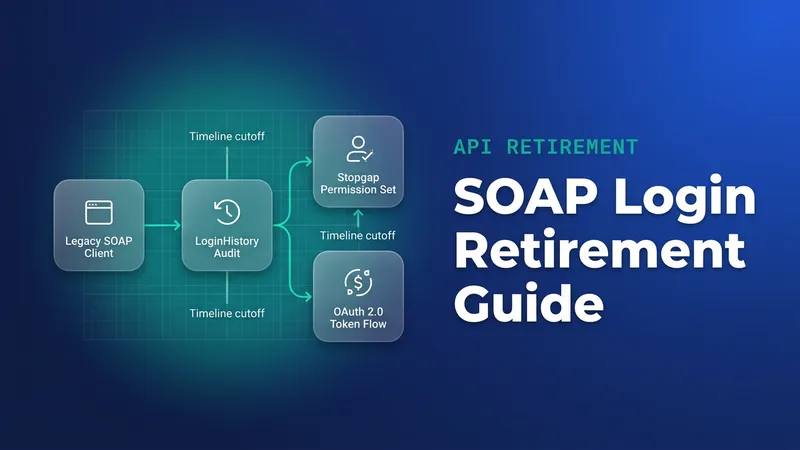
Salesforce SOAP Login Retirement: Two Deadlines, One Audit
Salesforce SOAP login retirement starts in Winter '27, when login() requires the Use Any API Auth permission, and...
 Integration
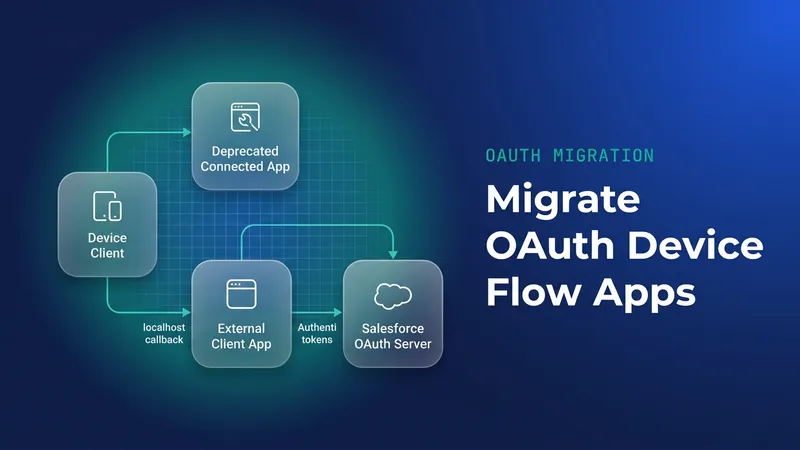
Salesforce OAuth Device Flow Ends for Connected Apps Nov 30
From 30 November 2026 the OAuth 2.0 device flow only works from local External Client Apps with a localhost callback,...
 Integration
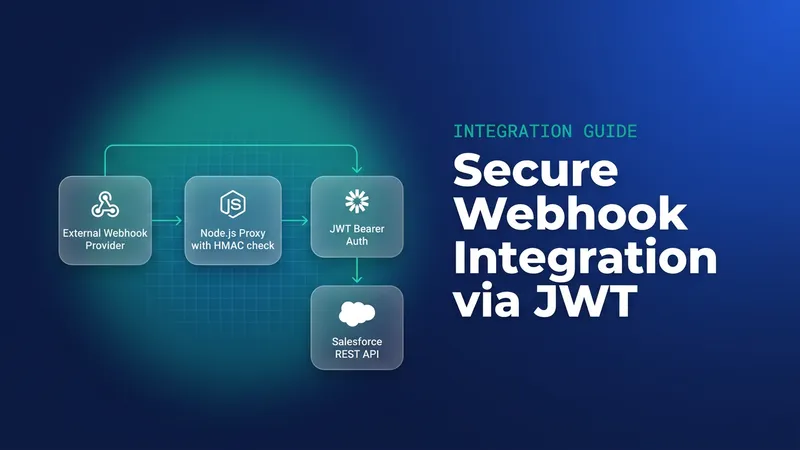
Salesforce Webhook Integration With JWT Bearer Flow
Salesforce has no inbound webhook listener, so third-party callbacks need a small service in front of the org. Building...
 Integration
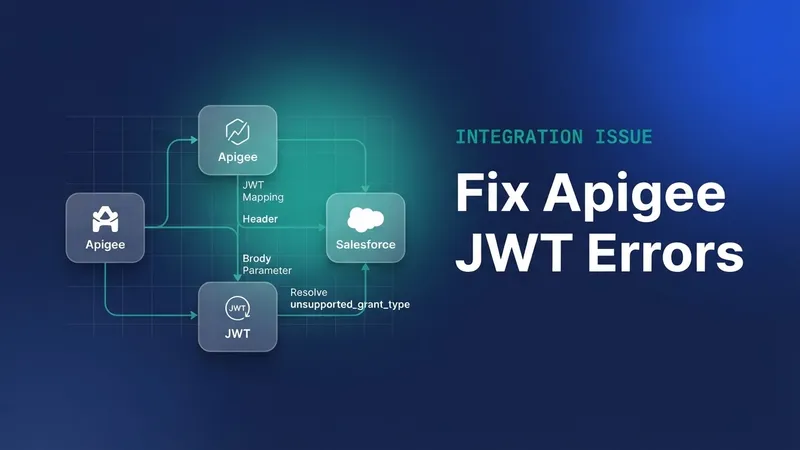
unsupported_grant_type: Fixing Apigee JWT Integration
The unsupported_grant_type error in Apigee usually comes down to how the OAuthV2 policy reads request headers against...
 Apex
Box.com Salesforce Integration: Apex Backend Guide
How to wire Salesforce up to Box.com in Apex: secure authentication, the file upload patterns that hold up, and error...
 Integration
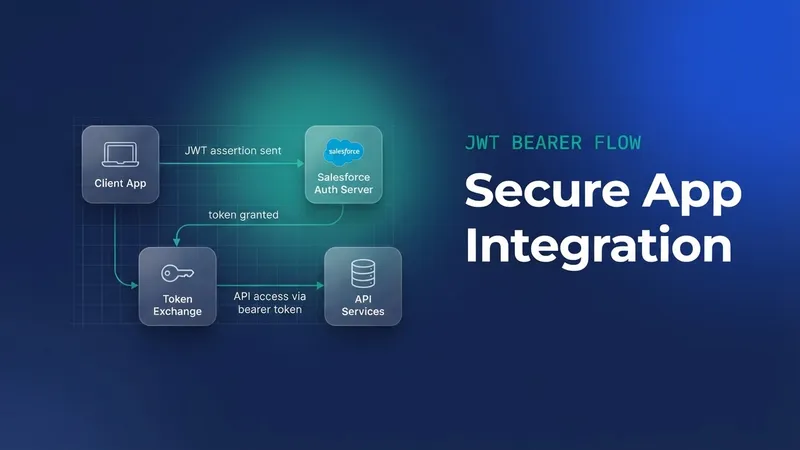
External Client App for Headless 360 MCP: Scopes and Setup
Headless 360's MCP server needs an External Client App with the mcp_api scope, refresh_token, and API v67.0 or later....
 Integration
Unattended Sandbox User Token Generation for CI/CD
Pulling access tokens for a pile of sandbox test users is a common CI/CD snag when the tests have to run as specific...